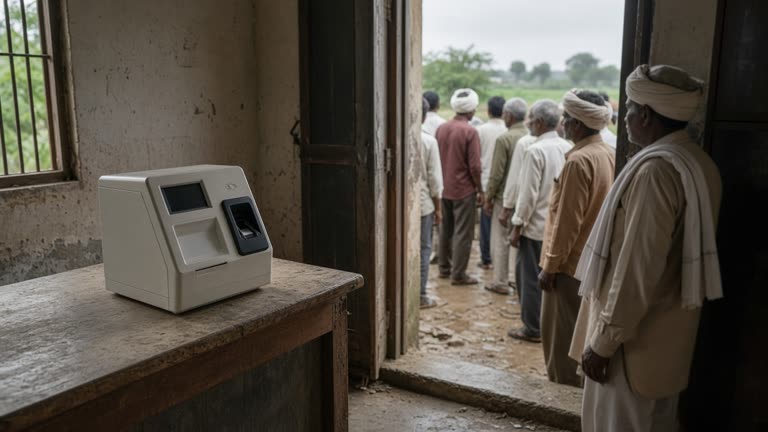
The Unique Identification Authority of India has opened a compressed round of Aadhaar masking and authentication API conformance labs ahead of the Diwali onboarding surge, when banks, payment apps, and employer KYC desks typically scale document intake. Registrars told InfoHandle that the September window is less about new policy than about proving that client software still masks the first eight digits of Aadhaar numbers, routes storage through reference keys in Aadhaar Data Vaults, and signs requests with hardware security modules before peak traffic hits.
What the labs are testing
UIDAI’s published compliance checklist treats masking as an outcome, not a marketing label. Entities must ensure that Aadhaar numbers collected on physical forms or photocopies show only the last four digits before archival, and that downstream systems do not retain full numbers outside an approved vault. Labs this month are running scripted uploads through vendor and in-house masking pipelines—image redaction, XML offline KYC packets, and e-KYC responses—to confirm that QR codes and digit strings match the authority’s latest authentication API specifications.
Engineers at two private-sector authentication user agencies said auditors are also probing API gateway controls: IP whitelisting, rate limits, and cross-origin restrictions that the checklist lists as mandatory. Error code 510 and 511 failures—invalid auth or PID XML—still trace back to teams running stale SDK builds, a recurring finding when staging certificates roll while production keys carry 2026 expiry dates on UIDAI’s developer portal.
Why Diwali timing matters
Seasonal hiring, gold-jewellery finance, and prepaid wallet top-ups push KYC queues from late September through November. MeitY-linked registrars estimate that onboarding volumes can jump 30 to 40 percent around festival bonuses, which is when partially masked PDFs leak through call-centre email if OCR pipelines fail. UIDAI’s masked Aadhaar FAQ is explicit: only the final four digits may remain visible on customer-facing copies, a rule that digital lenders sometimes treat as optional when rushing same-day approvals.
Circular 14 of 2025, which tightened Aadhaar Data Vault and HSM requirements, is now the backdrop for these labs. Requesting entities must host cryptographic operations in certified modules and map business tables to reference keys instead of raw Aadhaar numbers. Conformance reviewers are asking chief information security officers to demonstrate segregation between vault administration and application teams—a control gap that showed up in last year’s spot checks on smaller non-bank finance companies.
What integrators are changing
Large banks said they are freezing authentication client versions until lab sign-off, even where product teams wanted feature releases tied to UPI credit lines. Fintech aggregators are splitting masking into a dedicated microservice so that document forensics APIs cannot bypass vault write rules. Several are retesting against UIDAI’s pre-production certificates, which carry May 2026 expiries, to avoid a repeat of spring outages when certificate rotations collided with salary-account campaigns.
Smaller AUAs without dedicated compliance staff are pairing with certified ASPs, but UIDAI officials warn that outsourcing does not transfer liability. Sub-authentication user agencies must still run software digitally signed by the parent entity, and masking failures at a subcontractor still trigger suspension risk for the sponsor bank.
What to watch before November
UIDAI has not published a public headcount for failed lab slots, but industry groups expect a second lab week if certificate pinning issues persist on Android onboarding kits. Privacy advocates want the authority to publish aggregate pass-fail statistics by sector, arguing that Diwali volume should not become an excuse for storing unmasked scans in CRM buckets.
For customers, the practical test is simpler: any emailed or printed Aadhaar copy should show xxxx-xxxx in the leading positions. If it does not, the fault may sit in a masking API that never reached UIDAI’s conformance bench—exactly what this pre-festival schedule is meant to catch before millions of new accounts open.
Legal teams at two NBFCs said they are revisiting consent language on mobile apps so that masking failures trigger hard stops instead of silent uploads to object storage. UIDAI technical helpdesks reported higher ticket volume around certificate expiry dates listed on the developer portal, suggesting integrators are finally aligning staging and production trust stores before auditors arrive.