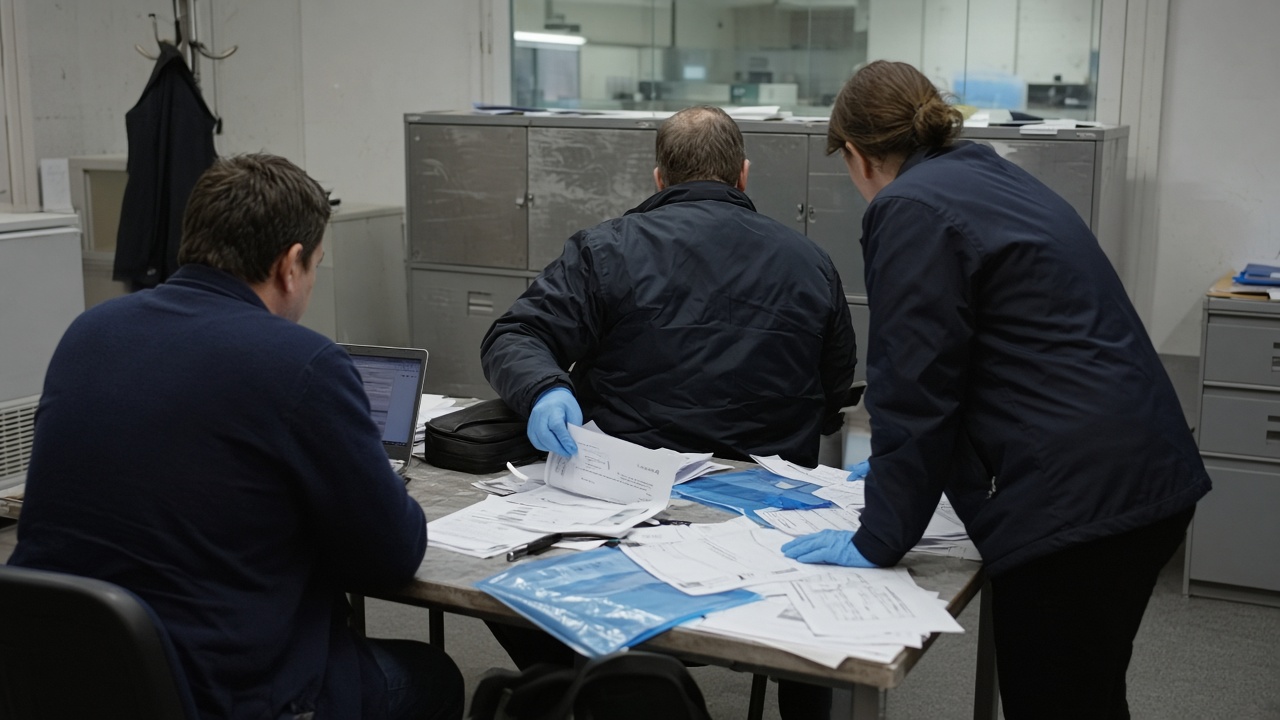
The Metropolitan Police cybercrime unit dismantled a business-email compromise ring that redirected payments from Solihull metal fabricators, according to a statement released early Wednesday.
What police allege
Detectives said the group infiltrated supplier email threads, inserted forged bank details on invoices, and laundered proceeds through cryptocurrency exchanges. Officers arrested four people in Coventry and London on suspicion of fraud and money laundering; inquiries continue.
Police attributed more than £2.3 million in attempted redirects to the crew over 14 months, with suppliers in the West Midlands reporting the highest losses. The Met stressed that figures are provisional until courts resolve cases.
How BEC crews operate
Business-email compromise attacks typically start with stolen credentials or spoofed domains that mimic finance teams. Fabricators in Solihull often run tight payment cycles, making a single successful redirect costly.
The National Cyber Security Centre advises segregating duties so no single inbox can change both purchase orders and payment files. Multi-factor authentication on cloud mail remains the baseline control.
Victims’ response
Trade bodies representing Midlands manufacturers said members are retraining accounts payable staff to call suppliers on known numbers before approving bank changes. Several firms told InfoHandle they are moving invoice approvals off email entirely for contracts above £50,000.
Insurers warned that cyber policies may not cover social-engineering losses if firms skip agreed controls. Brokers are seeing renewed demand for crime riders that explicitly include BEC.
Enforcement next steps
The Met said digital devices seized in the raids are undergoing forensic examination. Officers are working with Action Fraud to identify additional companies that may have paid forged invoices without realising.
No charges have been filed yet; suspects remain in custody within statutory limits. Police asked any West Midlands supplier receiving unexpected bank-change requests since 2024 to contact the investigation team via Action Fraud.
Prevention checklist
Official guidance remains unchanged: verify payment changes out-of-band, monitor domain registrations similar to your company name, and restrict mail-forwarding rules that attackers abuse. The Solihull case shows that even industrial firms with thin IT teams are lucrative targets when inboxes are shared.
Regional coordination
West Midlands Cyber Resilience Centre offered free workshops after the arrests, walking finance teams through domain monitoring tools. Several Solihull firms said they would join the programme after paying duplicate invoices last year.
Accountants serving Midlands manufacturers circulated refreshed checklists urging dual approval on any bank-detail change, even when emails appear to come from known suppliers. The Institute of Chartered Accountants said it would host a webinar with Met cyber officers next month.