The Ministry of Economy, Trade and Industry certified a ransomware response playbook on Wednesday that regional electric utilities must adopt—or explain why they have not—before renewing cyber insurance policies tied to government-backed resilience loans. The document, co-authored with the National center of Incident readiness and Strategy for Cybersecurity (NISC) and the Organization for Cross-regional Coordination of Transmission Operators (OCCTO), targets operators too small to run twenty-four-hour security operations centers but large enough that a weekend encryption event could black out prefectural feeders.
Why regional utilities moved up the queue
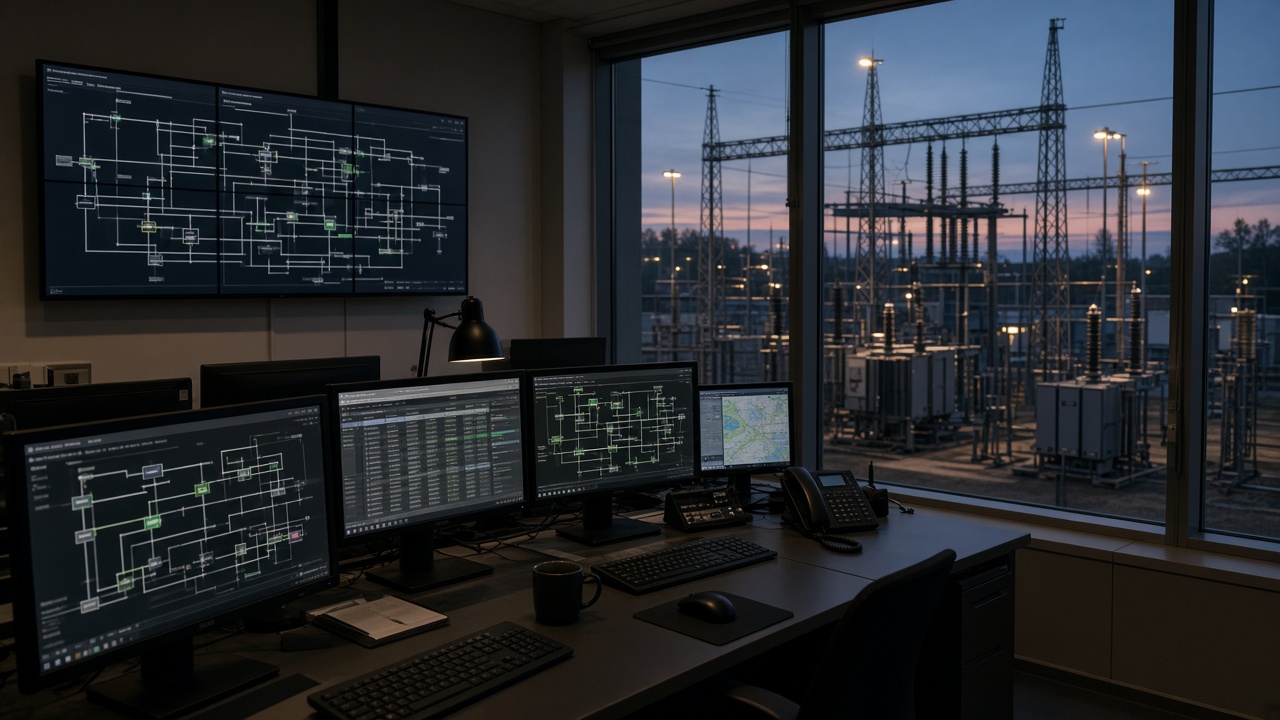
Tokyo’s investor-owned giants absorbed headlines after global ransomware waves, yet METI officials said incidents reported through OCCTO’s confidential channel rose fastest among municipal power and rural cooperatives between 2024 and 2026. Attackers shifted from billing-system phishing to remote-desktop paths into distribution management systems that were never meant to face the public internet.
Last winter a Kyushu cooperative lost visibility into four substations for eleven hours after criminals encrypted historian servers; operators reverted to manual switching without customer injuries, but the near miss convinced METI that playbook uniformity mattered more than another advisory PDF.
What certification requires
The certified playbook mandates immutable offline backups tested quarterly, separate credential stores for office IT and operational technology, and a four-hour decision tree for isolating SCADA segments without tripping wide-area protection relays. Utilities must run tabletop exercises with prefectural disaster officers and document vendor remote-access lists—a mundane control that failed in multiple 2025 cases when forgotten VPN accounts stayed enabled after maintenance.
Insurance syndicates participating in METI’s resilience credit line said they will treat certification as a premium discount input starting April 2027. Uncertified utilities can still operate, but loan covenants on grid-hardening bonds will ask boards to sign exception letters reviewed by OCCTO.
OT realities on thin staffs
Regional utilities often employ a handful of engineers who maintain both Windows patch cycles and relay settings. The playbook allows phased segmentation: prioritize high-voltage control networks first, defer advanced endpoint detection on field laptops until 2027 if budgets require it, but forbid flat networks that let ransomware jump from HR printers to feeder automation in one hop.
NISC published anonymized wiring diagrams showing how a Hokkaido operator rebuilt demilitarized zones using commodity firewalls already procured for compliance with the Act on the Protection of Personal Information. METI emphasized low-cost patterns because capital spending on new substations already competes with typhoon hardening.
Coordination with transmission and nuclear neighbors
OCCTO’s role is synchronizing playbook steps with wider grid restoration. If a regional utility isolates SCADA to stop spread, transmission operators need standardized status codes rather than ad hoc phone trees. The playbook embeds OCCTO’s existing outage data exchange formats so encrypted utilities can publish “manual operation” flags without exposing internal network details.
Utilities near nuclear sites must notify designated liaison officers within ninety minutes under separate nuclear disaster law; the ransomware playbook cross-references those clocks so cyber incidents do not wait until daylight for legal review.
Vendor and municipal oversight
Prefectural governments that own municipal utilities face new disclosure templates: city councils will receive annual attestation summaries instead of raw network maps, a compromise after local politicians worried about publishing attack surfaces. Vendor contracts for SCADA maintenance must include forty-eight-hour patch-or-isolate clauses; METI listed three overseas remote-support firms whose Japan customers failed that test in audits this summer.
What critics want next
Consumer advocates said certification should eventually cap ransom payments insurers reimburse, mirroring debate in the United States. METI stopped short, arguing Japan’s smaller utilities sometimes pay to restore billing data quickly during heat waves. Privacy scholars asked whether backup drills duplicate customer usage data unnecessarily; the playbook requires hashed samples rather than full tariff databases in test restores.
Silver Week stress test
Officials urged utilities to finish first certification audits before Silver Week, when maintenance crews are thin and phishing lures reference travel refunds. Cyber insurers noted that holidays correlate with threefold help-desk ticket spikes when part-time staff approve fake password resets.
For Japan’s regional grid, the policy shift is administrative but consequential: ransomware defense becomes a balance-sheet line item with a METI stamp, not a volunteer IT project that waits until after the next typhoon season.