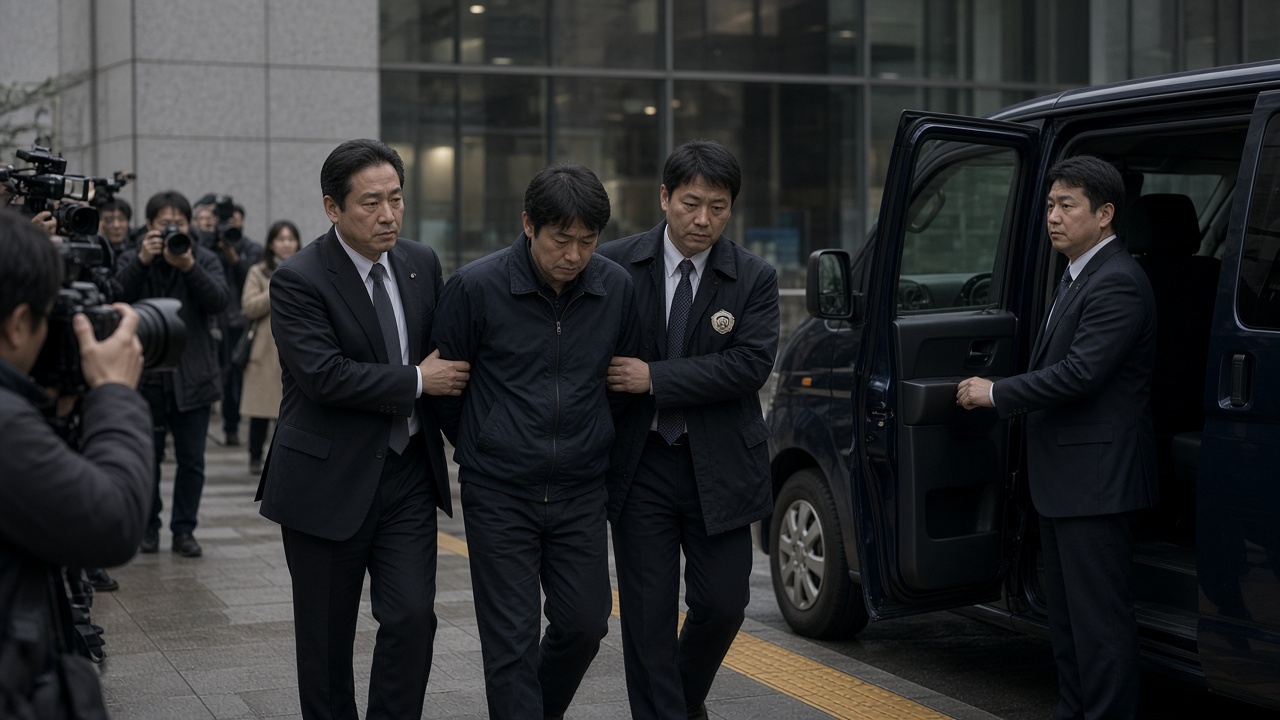
Japanese authorities extradited a Russian national suspected of helping run the Qilin ransomware group to Germany this week, after locating him inside Japan on a warrant connected to an attack that encrypted a German company's data, investigative sources told domestic media on Tuesday.
The handover marks a rare public win for cross-border cooperation against a crew that has claimed high-profile victims worldwide, including Japanese beverage giant Asahi Group Holdings, which blamed Qilin-linked operators for a major systems outage in 2025. German investigators had been searching for the suspect in connection with a separate intrusion before alerting Tokyo that he might be in the country.
How the arrest unfolded
According to accounts attributed to the National Police Agency and prosecutors, German authorities shared intelligence that placed the man in Japan. Japanese investigators tracked his movements, detained him on the basis of the German request, and arranged transfer after German officials traveled to complete extradition procedures.
Police declined to release the suspect's name or the exact date of the transfer, citing ongoing inquiries in both countries. Sources described him as a "key member" of Qilin's operational structure rather than a low-level affiliate, though no indictment documents were made public in Tokyo on Tuesday.
Qilin, also tracked under the name Agenda, has been tied to double-extortion schemes in which attackers steal files before deploying encryption, then pressure victims with leak threats. Security firms have linked the group to incidents across manufacturing, healthcare and consumer brands in Europe and Asia.
Japan's ransomware surge
The extradition lands as Japan reports record ransomware volumes at home. The National Police Agency said 123 ransomware cases were confirmed in the first half of 2026, the highest six-month total the agency has published. Business leaders have pressed the government to streamline mutual legal assistance after several incidents in which operators appeared to move between jurisdictions faster than warrants could follow.
Justice Ministry officials have been revising procedures for holding foreign suspects when victims and servers sit in multiple countries. Tuesday's transfer is likely to be cited in Diet security briefings as evidence that Tokyo will honor partner warrants even when the underlying crime targets a company outside Japan.
What prosecutors still need to prove
German prosecutors now face the task of connecting the suspect to specific malware deployments, cryptocurrency cash-out trails and communication channels Qilin affiliates used to negotiate ransoms. Japanese police said their domestic inquiry continues into whether the man or associates accessed Japanese networks or recruited local money mules.
Asahi Group has not commented on whether investigators have tied the extradited suspect to the 2025 outage, and company spokespeople stressed that civil recovery efforts remain separate from the criminal case. Cybersecurity agencies in the United States and Europe have listed Qilin among the most active ransomware brands this year, warning that affiliates rotate hosting and rebrand quickly when law enforcement closes in.
For German authorities, the extradition provides a live defendant who can be questioned about infrastructure Qilin used against the unnamed corporate victim that triggered the original warrant. For Japan, the case tests how quickly police can act when a foreign partner identifies a suspect on Japanese soil — a scenario officials expect to repeat as ransomware crews treat Tokyo's visa rules and transit hubs as potential hideouts.